

Posts on this page:
- Active Directory registered OID sometimes is not visible to clients
- Key Recovery Agent certificate management
- How to save disappearing MSDN and TechNet blogs with PowerShell
- PowerShell PKI Module v3.3.0 is out!
- PowerShell PKI Module v3.2.7 is out!
Hello world! Recently, a fellow guy asked a question why freshly registered OID is not visible in his app, while other applications see that OID. Today I will explain some nuiances on how AD-registered OIDs are propagated to clients and how OID caching works.
The OID metabase
Every Windows installation ships OID (Object Identifier) mapping table, which divides various OIDs into a fixed set of OID groups:
| Group ID | Group Name | Description |
|---|---|---|
| 1 | HashAlgorithm | Contains hash algorithms, such as md2, md4, md5, SHA1, SHA256, SHA384, SHA512 and so on. |
| 2 | EncryptionAlgorithm | Contains symmetric encryption algorithms such as DES, 3DES, AES128, AES256 and so on. |
| 3 | PublicKeyAlgorithm | Contains public key algorithms, such as RSA, DSA, ECC, ECC curves, ML-DSA, ML-KEM and so on. |
| 4 | SignatureAlgorithm | Contains composite signature algorithms, such as sha1RSA, sha384ECDSA, ML-DSA-44, and so on. |
| 5 | Attribute | Contains X.520 RDN attributes, such as CN, E, C, Street, DC and so on. |
| 6 | ExtensionOrAttribute | Contains X.509 extension OIDs and CMS/PKCS#9 attributes, such as "Message Digest". |
| 7 | EnhancedKeyUsage | Self-explanatory, EKUs, such as "Server Authentication", "Code Signing" and so on. |
| 8 | Policy | Contains certificate policy OIDs, see RFC 5280 §4.2.1.4. Example: "All Issuance Policies" |
| 9 | Template | Contains ADCS certificate template OIDs. |
| 10 | KeyDerivationFunction | Contains KDF OIDs, such as ECDH_STD_SHA1_KDF |
Any OID in the table consist of four parts:
Read more →
Hello everyone!
This a good time for a new blog post! Today I want to share some thoughts on Key Recovery Agent (KRA) certificate management.
What is KRA and Key Archival
Let's refresh what private key archival is in AD CS context. Key Archival is the process of securily storing subscribers' (clients) private key in CA database for backup purposes should client loose access to private key. Key archival is primarily used to implement a centralized long-term backup process for encryption keys (email, EFS, document encryption).
The whole idea may not be apparent from the first look, but here is a strong reason: encryption keys are used to decrypt documents/files/emails even after their expiration, so you may need encryption key after its expiration. Expired certificates are not normally backed up as part of regular backup process or stored in long-term backup set. If certificate is expired, we normally renew it and delete old one. And you will be stuck if such encryption certificates and their keys are lost. This is why Microsoft implemented a separate encryption certificate backup process and store them in CA database. CAs are long-living entities, can live for decades and survive multiple migrations. And it can be easily backed up with regular backup process, because it will store a complete history of CA DB content, including historical one.
While it may look insecure, storing private keys in database is never a good idea, right? And this is where Key Recovery Agent (KRA) comes to a play. All private keys stored in CA database are encrypted with one or more KRA certificates. And even if you steal CA database and dump it, client private keys will be stored in encrypted blobs and CA/attacker has no access to KRA keys to decrypt client keys. Here is a timeline diagram that shows key archival process:
Read more →
Hello readers!
Blogs are dying
Last week I was surprised when got the following message on Microsoft Blogs (eaxmple: https://blogs.technet.microsoft.com/crypto):
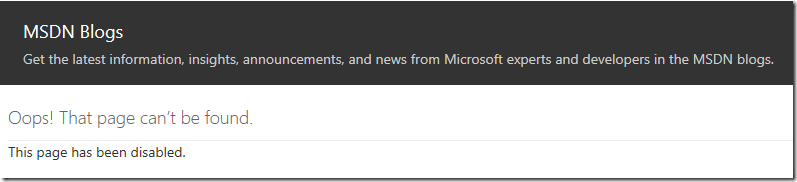
After some investigation, more disabled blogs were found. I tried to find any information about what is going on, but not much luck. All I was able to find is the fact that Microsoft is retiring their TechNet and MSDN platforms and move to..yes, another blogging engine. Though, not all blogs are moved. There are various rumors (not yet official) and they suggest that only most popular and trending (Azure!) blogs will be migrated. The rest blogs will be wiped. Silently. Other rumors suggest that it is blogs owner’s responsibility to move their blog to a new platform. Keep in mind, these are just rumors, the fact is that blogs silently disappear: https://blogs.technet.microsoft.com/brandonlinton/2018/11/05/retirement/. There was no official announcement from Microsoft about the trend or blog decommission schedule. Further investigation revealed that MSDN blogs are mosing to DevBlogs and TechNet blogs are moving to TechCommunity.
Read more →
Hello everyone!
Yesterday I pushed new PSPKI release with version number v3.3.0. New version is even more stable and even more powerful. More technical change list is moved to dedicated article: Release notes for PSPKI v3.3.0. In this (and, possibly next) blog post I would like to outline major changes/improvements to this release.
ADCS Database row presentation
I bet that ADCS database access is one of the most popular features people love in my module. And there are reasons: I put a lot of efforts to simplify access to CA database and provide flexible filter options. For example, get certificates that will expire in next 30 days:
Read more →
Hello world! Last time (year or so) I was busy on anything else but my module. Now I’m happy to announce that the project isn’t died, it is alive and new version is published.
This version doesn’t bring new commands, nor deprecate any. I think, command list is well-established and I don’t see anything useful to add. People doesn’t ask either. However there are things to work with code: refactor, optimize, make it cleaner and so on. Let’s look at what I’ve done here:
PowerShell Gallery
- Moved sources from CodePlex to GitHub
Initially, project was hosted at CodePlex which is died now. I moved all my sources to GitHub, documentation to my web site and used CodePlex as module download place.
- Moved binaries to PowerShell Gallery
Since CodePlex is done, the only real option to ship binaries was to use PowerShell Gallery. It is something new to me (I never used it till today) and was a bit lost there. But it appeared more easier than I thought. Starting with v3.2.7, the module is available on PowerShell Gallery: PSPKI. Please, provide feedback on your experience with getting PowerShell PKI module from gallery.
- Deprecated MSI Installer
In the past, I used MSI installer to ship the module. It is still very good option to do that, because you can use various tools, like group policies or ConfigMgr to deploy the module within organization. Thanks to Caphyon Advanced Installer and their free NFR license (as a part of my Microsoft MVP award) I was able to do that. And their tool was really great and easy to use. However, my MVP award options are uncertain and PowerShell Gallery is an acceptable tradeoff, so there is no big need in MSI anymore.
Fixed bugs
Read more →